
When choosing instruments to safe your APIs, it’s essential to look for capabilities that transcend basic access management. Gravitee’s event-native API Gateway provides a strong set of options that address each security and operational resilience throughout REST, Kafka, WebSocket, and MQTT. Defending APIs requires a multi-layered defense strategy, with every kind of tool addressing specific vulnerabilities or risks. Here’s a breakdown of the most important classes and the way they contribute to a safe API ecosystem—with an emphasis on the important function of API gateways. Having previous information on API attacks is essential for safety teams to boost their defense methods. Traceable’s security https://bussinessfair.info/strategic-management-best-practices-for-2024.html information lake supplies powerful capabilities much like EDR instruments used by enterprises for years.

Real-time Monitoring & Analytics
AppTrana leads the greatest way with its innovative approach to risk-based, absolutely managed API security options. For organizations in search of an additional layer of safety including managed services, you’ll have to go for WAAP like AppTrana which bundles managed services. In the premium plan, the managed companies https://freeassangenow.org/the-evolution-of-cybercafe-technology-redefining-the-digital-social-experience/ staff acts as an extension of your SOC staff and customizes guidelines that seamlessly combine with your corporation requirements, guaranteeing zero false positives. AppTrana’s approach to API security combines dynamic scanning and manual penetration testing to search out vulnerabilities earlier than hackers do.
Cloud Security Sources
Imperva combines its in depth net application security experience with specialised API protection capabilities per teh maturity mannequin. The solution supplies multilayered safety via its cloud-based infrastructure, utilizing its international risk intelligence community to protect APIs towards emerging threats. Gravitee API Gateway is an event-native API administration solution that handles each synchronous and asynchronous APIs. It permits organizations to handle the API lifecycle whereas supporting event-driven architectures alongside traditional API patterns. The gateway processes giant volumes of traffic effectively and offers a unified layer for making use of policies. Sturdy authentication and authorization mechanisms are essential to defend towards frequent API threats similar to credential theft, privilege escalation, and knowledge exfiltration.

Api Gateway–integrated Instruments
This implies that threats are detected and mitigated immediately with out the necessity to send knowledge to separate instruments for evaluation. With WAAP, there’s no delay in defending internet applications and APIs, making certain efficient and effective safety measures. Conventional API security options — like WAFs and API gateways — require documentation to configure safety. AppSec teams are often not conscious of those APIs, which is why they’re called shadow APIs.
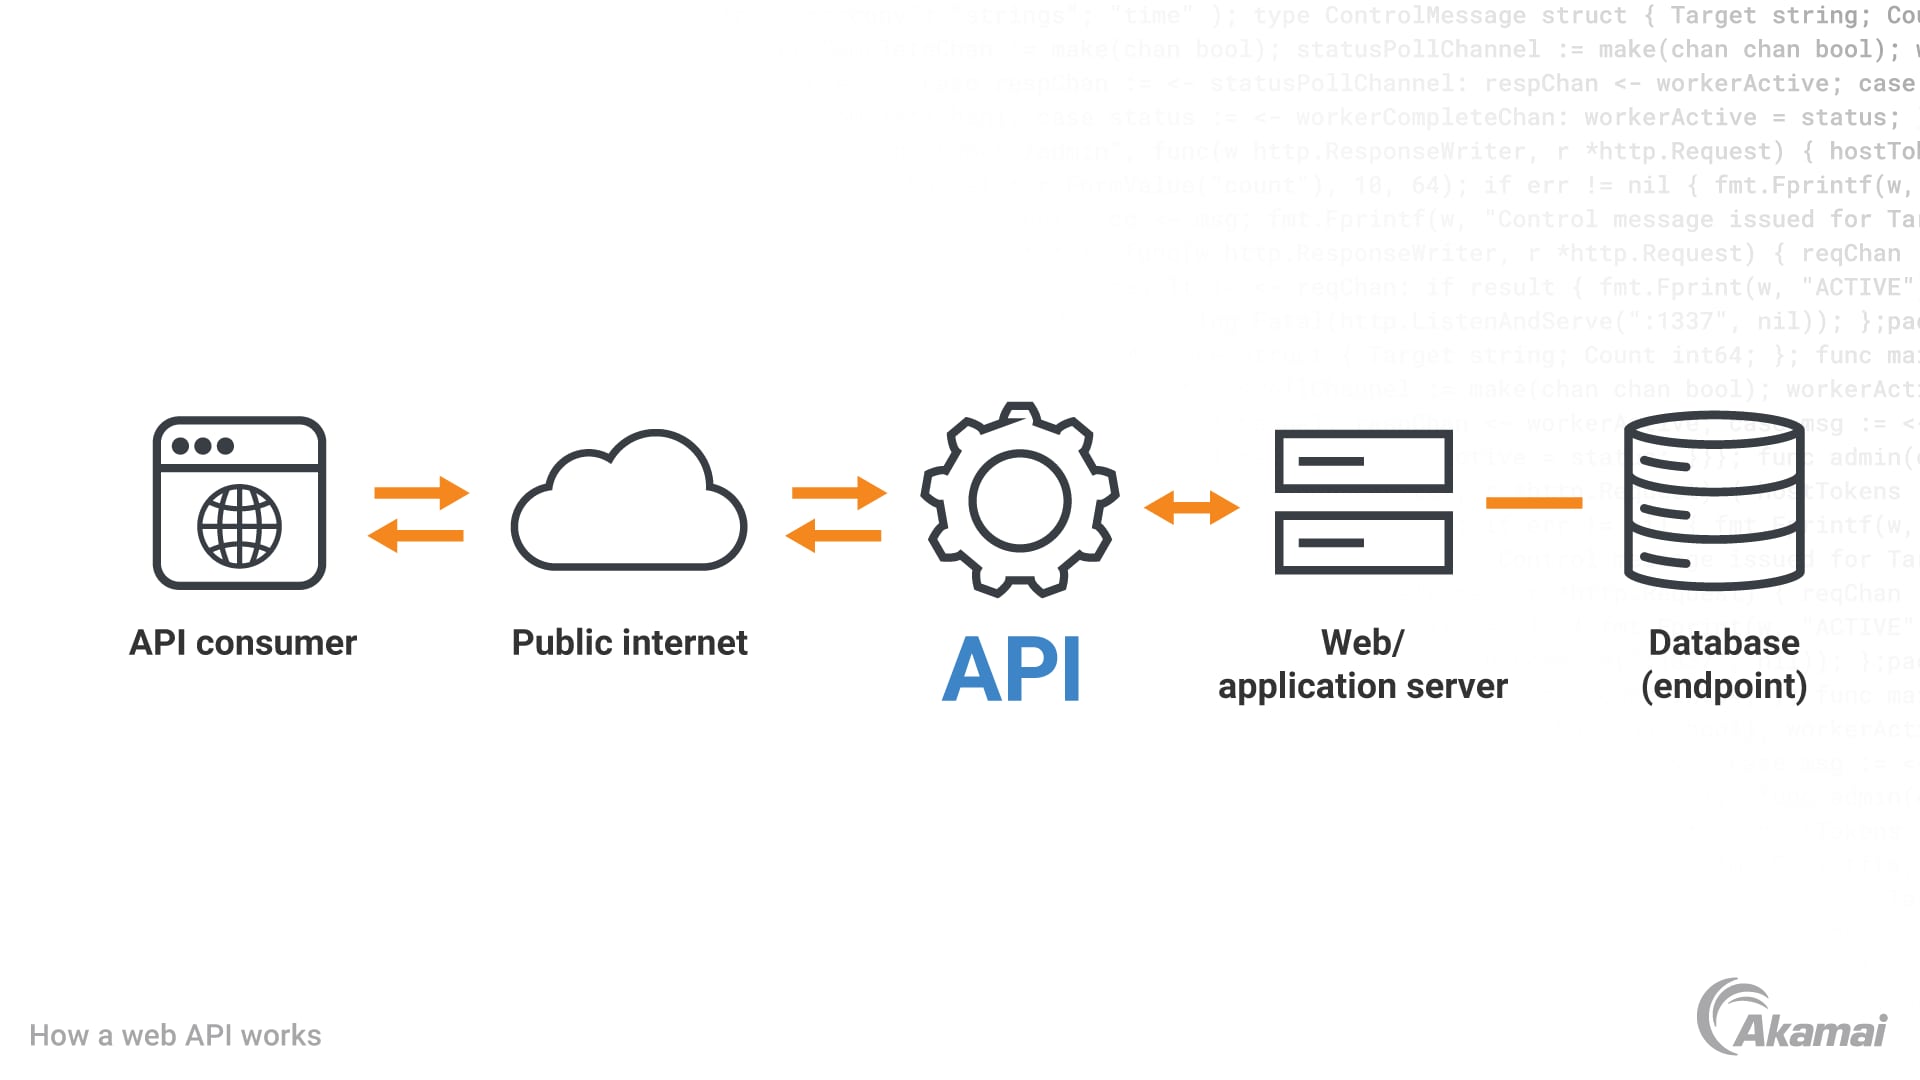
- API endpoints are essential as a end result of they supply the exact location of the info or resources the API is accessing and be positive that the system speaking with the API is functioning optimally.
- These tools shine mild on shadow APIs and reduce blind spots that attackers might exploit.
- 42Crunch is a strong API security platform designed to bolster API security posture, automate testing within CI/CD pipelines, and enforce security policies.
Remediate what really issues using our unmatchable inventory of every API and detected vulnerability, ranked by business threat. Organizations can inadvertently create zombie APIs when releasing a new API version — they depart the original model in production quickly to ease migration, then neglect to decommission it. These abandoned endpoints remain reside, usually with outdated safety controls, making them attractive targets for attackers who know legacy techniques are not often monitored. See the complete historical past of every API change to raised perceive how dangers had been introduced throughout the complete API lifecycle. When a vulnerability surfaces, the change log reveals precisely which commit introduced it, which developer made the change, and what the API looked like earlier than – so remediation is fast and exact.